01
Windows /
Active Directory
- Kerberoasting & AS-REP
- BloodHound path analysis
- NTLM relay & coercion
- AD CS abuse
/ About
My main platform is HackTheBox: 80 machines across Easy → Insane. I write a machine up after it retires, because explaining the chain is where the learning actually sticks.
Identity
Certifa
Mike · 24 y/o
Location
Utrecht
Netherlands
Studying at
Hogeschool Utrecht
Cybersecurity & Cloud BSc
Primary platform
HackTheBox
Master · lvl 75 · global #382
Attack OS
Kali Linux
tmux, vim, burp
The long version
It started on a Nintendo DS Lite with an R4 card. A flashcart that let the console run things Nintendo never approved. I was young enough that I didn't really know what I was doing. I just knew the rules turned out to be negotiable. After that it was Minecraft servers, CS:GO cheats, Runescape bots, game files pulled apart to see what was inside. Different games, same question every time: where's the advantage nobody's using.
Eventually I stopped asking that about games. The family PC and the router at home were the first things I broke that weren't a toy, and the interesting part wasn't that they broke. It was that it had been possible the whole time and nobody had bothered to look.
Why know a little when you can know it all.
The handle doesn't mean anything, by the way. I needed one, Certifa sounded right, and it stuck. I'd rather tell you that than invent a story for it.
None of this is school, either. My course is networking, cloud, enterprise infrastructure, automation. Genuinely useful, and it gave me a structure I wouldn't have built on my own. But the offensive side happens next to it, on my own time. I learn properly when I decide to, and this is the thing I decided to. What I read about gets rebuilt at home, on a Windows Server 2022 domain controller and two workstations, so a chain I've only read about becomes one I've actually run. Anything I do more than twice ends up in Python. nmapfullscan.py came out of that: sweep every TCP port, parse what actually answered, then run service detection on only those. It exists because I got tired of typing the same two commands and mis-copying port lists between them.
Why this and not something easier: it's the same feeling as a boss going down in a Souls game. You throw yourself at the same wall for hours, it finally gives, and for about thirty seconds you're the best there is. Relief and dopamine in the same hit. Then you go looking for the next wall.
I'm not tidy about it. I move faster than I document. Three steps past a foothold before I've written down how I got there, then re-deriving the whole thing later for the writeup. I've started taking notes while the box is still open instead of after. And I've spent three days on one machine rather than take the hint, which I'd call stubbornness if it didn't keep working.
Which is why the writeups exist. Explaining a chain to someone else is where the learning actually sticks, and it's the part most people skip. It's also the honest picture of the job: mostly reading, failing, and writing things down. Not a hoodie, not a green screen, and not illegal. These are rented machines built to be broken.
The hard part isn't the boxes. It's that almost nobody I know offline understands what I do. I come out of a room having got domain admin and it doesn't translate. The people who get it are online, and they're a lot of the reason I've kept going. And I'm impatient: there are people younger than me with certs and seats, and I don't have the seat yet. That keeps me up more than any box does.
CJCA landed in September 2026, the first one on the board. CPTS is next, CCNA after that. I'd rather show the work than the paper, but I'm going to have both. What I'm after is a first red-team seat: an internship or a junior role, against something real, with people better than me in the room. Not famous. Just genuinely good at this, and still enjoying it in five years.
The kit · four things I keep going back to
01
02
03
04
The paper · CJCA earned
CJCA
CPTS
CCNA
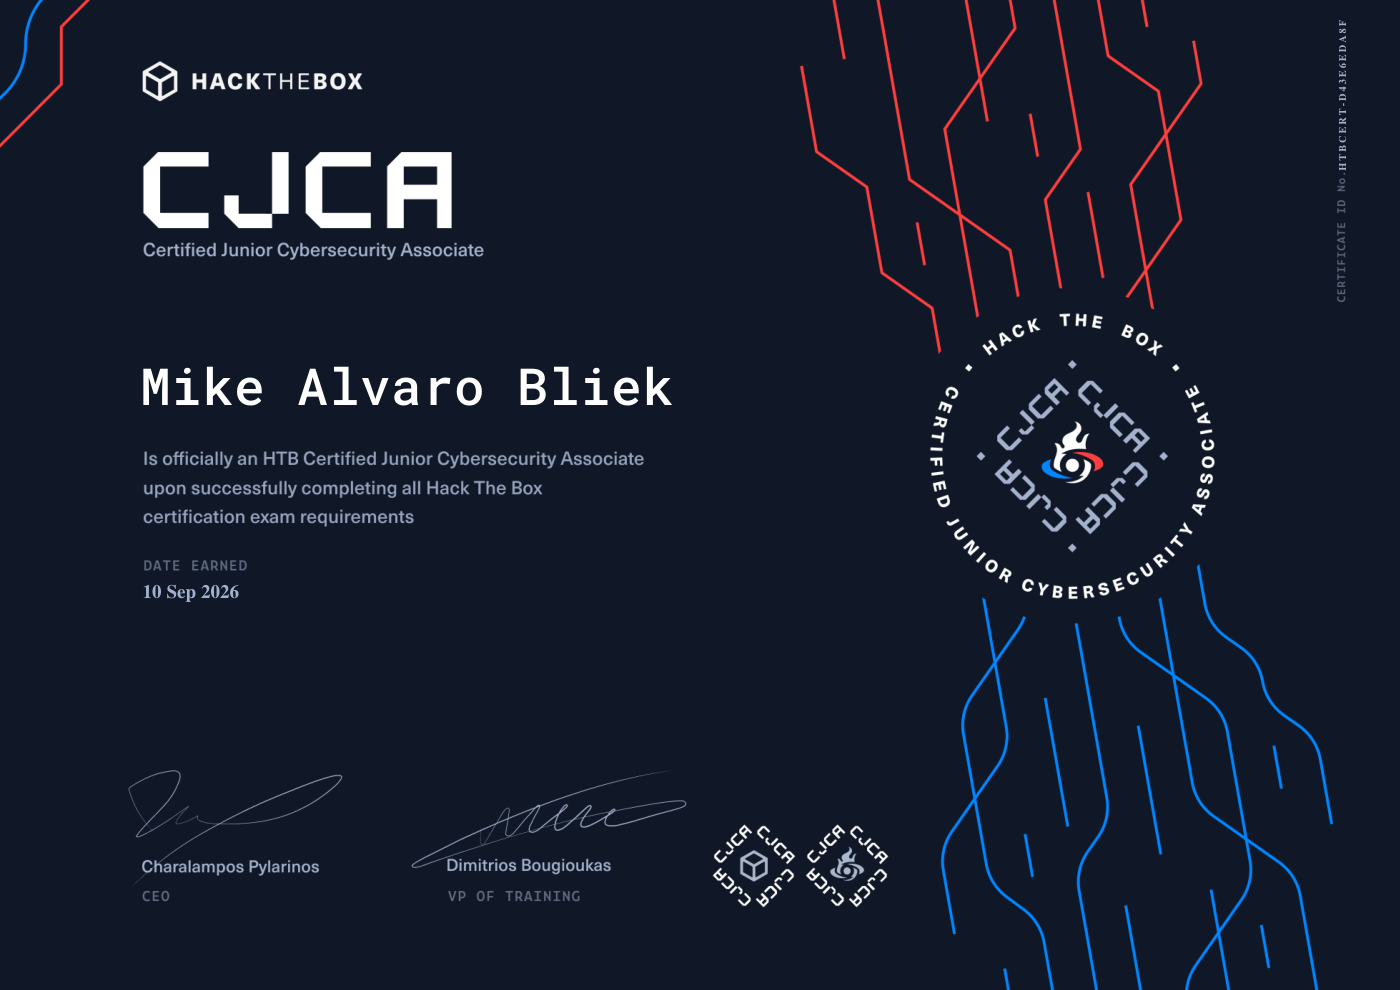
One down, two to go. Until the rest land, the writeups are the evidence.
Off the clock
Training
The gym, most days. Same appeal as a box. You either moved the weight or you didn't, and no amount of talking about it changes the number.
Company
A calico called Laila has watched more of these boxes fall than anyone else, and has never once been impressed.
Games
Bloodborne was my first Soulslike and it's still the one. Elden Ring is the most beautiful thing I've played. Both teach the same lesson as a hard box: the wall moves when you do.
Eye
I care about art and design more than most people in this field. That's the only reason this site doesn't look like every other security portfolio.